NIS2 and collaboration tools: what companies should check now
Germany’s NIS2 implementation act has been in force since December 2025. We summarize who is covered, which obligations apply and which questions to ask collaboration tool vendors.
With the transposition of the EU’s NIS2 directive into German law, the number of companies with statutory cybersecurity obligations has grown considerably: according to Germany’s Federal Office for Information Security (BSI), it now supervises around 29,500 entities, up from about 4,500. The obligations also affect the tools teams use every day – file storage, chat, video meetings. This article summarizes who is covered, which obligations apply and what this means when choosing collaboration tools. Status: October 2026.
Status of NIS2 implementation in Germany
Directive (EU) 2022/2555 was due to be transposed into national law by 17 October 2024. Germany did so with the Act implementing the NIS2 Directive and regulating essential principles of information security management in the federal administration. According to the BSI, it was promulgated on 5 December 2025 and entered into force on 6 December 2025. The obligations for companies are set out in the revised BSI Act (BSIG).
According to the BSI’s FAQ, there is no general transition period. Under Section 33 BSIG, covered entities must register with the BSI no later than three months after they first fall within scope. Registration takes two steps: first via “Mein Unternehmenskonto” (based on the ELSTER tax portal), then in the BSI portal. For entities covered from the date of entry into force, this deadline ended in early March 2026.
Who is covered by NIS2
Companies must check for themselves whether they fall within scope. What counts is the sector under Annexes 1 and 2 of the BSIG and the size under Section 28 BSIG:
| Particularly important entity | Important entity | |
|---|---|---|
| Sectors | Annex 1, e.g. energy, transport, finance, health, water, digital infrastructure, space | Annex 1 or 2; Annex 2 includes e.g. waste management, chemicals, food, manufacturing, digital service providers, research |
| Size | at least 250 employees, or annual turnover above €50 million and balance sheet total above €43 million | at least 50 employees, or annual turnover and balance sheet total each above €10 million |
| Fines up to | €10 million; for total turnover above €500 million, up to 2% of worldwide turnover | €7 million; for total turnover above €500 million, up to 1.4% of worldwide turnover |
There are also special cases, such as operators of critical facilities, which always count as particularly important entities, and some providers for which size does not matter, for example DNS service providers. The fines are set out in Section 65 BSIG. The BSI offers a non-binding first assessment with its NIS2 applicability check (in German).
Even companies that are not covered themselves may feel the effects: the BSI points out that the rules can indirectly affect suppliers, for example through contractual requirements from covered customers.
The key obligations at a glance
Risk management (Section 30 BSIG)
Covered entities must take appropriate, proportionate and effective technical and organisational measures and document compliance. Section 30(2) BSIG lists ten minimum areas, including:
- policies on risk analysis and information security,
- incident handling,
- business continuity, such as backup management and disaster recovery,
- supply chain security, including relationships with direct suppliers and service providers,
- policies on the use of cryptography,
- personnel security, access control and management of ICT systems,
- multi-factor or continuous authentication and secured voice, video and text communication.
Reporting obligations (Section 32 BSIG)
Significant security incidents must be reported to the joint reporting office of the BSI and the Federal Office of Civil Protection and Disaster Assistance, in stages under Section 32 BSIG:
- early initial report no later than 24 hours after becoming aware,
- incident report with an initial assessment no later than 72 hours,
- interim report at the BSI’s request,
- final report no later than one month after the incident report; if the incident is still ongoing, a progress report first.
Management responsibility (Section 38 BSIG)
Management bodies must implement the risk management measures and oversee their implementation. If they breach these duties, they are liable to their entity for culpably caused damage under the rules of the applicable company law. They must also attend training regularly (Section 38 BSIG).
What NIS2 means when choosing collaboration tools
A collaboration tool is a direct service provider in terms of supply chain security. Art. 21(3) of the directive requires entities to take into account the specific vulnerabilities of each direct supplier and the quality of its products and cybersecurity practices. The BSI stresses in its FAQ that contracts alone are not enough. These questions help with the assessment:
- Sign-in: can multi-factor authentication be made mandatory for all accounts, including external participants? Is single sign-on with your identity provider available?
- Access control: can rights be assigned granularly, and do departing employees lose access automatically?
- Cryptography: how is data encrypted in transit and at rest, and who manages the keys?
- Traceability: is there a tamper-evident log that helps investigate an incident?
- Business continuity: how often are backups made, are restores tested, and can you get your data in standard formats at any time?
- Incidents at the vendor: how quickly will the vendor inform you about security incidents? Your own 24-hour deadline starts when you become aware.
- Communication: do chat and video meetings run on systems whose security you can assess?
- Supplier chain: which sub-processors are involved, and where is data processed? See our “DPA checklist: reviewing data processing agreements for cloud tools” (coming on December 2, 2026).
- Evidence: which certificates or audit reports exist, and for which scope?
It also helps to look at the number of tools in use: every additional service is another supplier in your chain that you need to assess and monitor. How to bring in external people in a controlled way is covered in “Guest access or own account? How to bring in external users” (coming on November 25, 2026).
Where nest54 fits – and where it does not
nest54 can provide individual technical building blocks that matter in such an assessment:
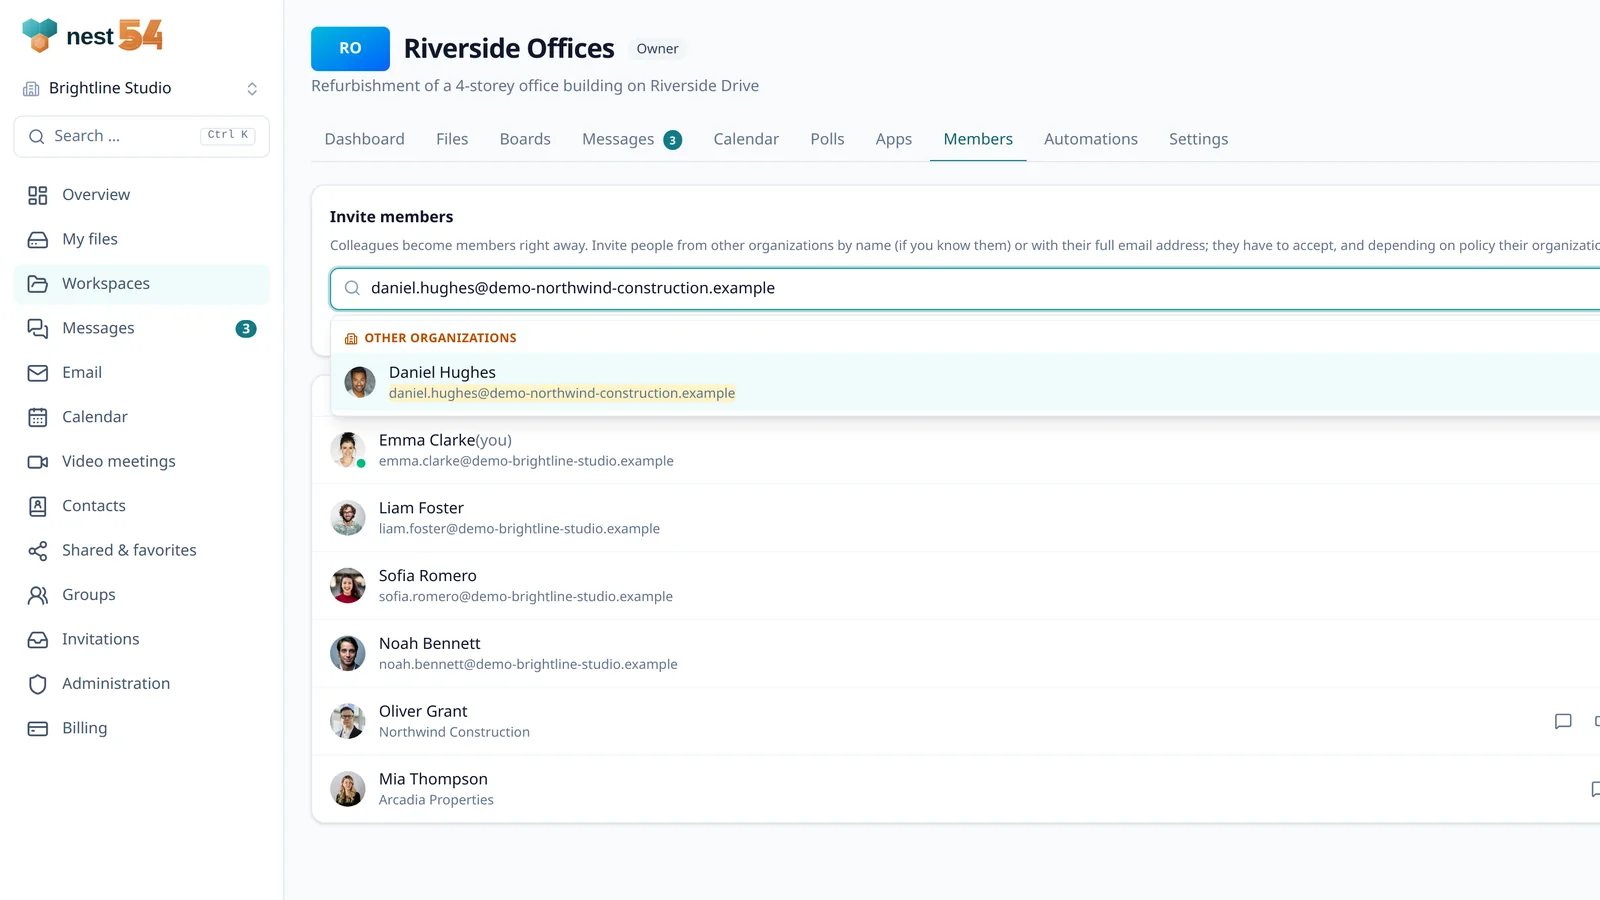
- two-factor authentication with an app or passkey, mandatory per organization and per workspace,
- single sign-on via OpenID Connect or SAML 2.0 and SCIM 2.0, so your identity provider creates and deactivates accounts,
- file encryption with a separate key per organization,
- a hash-chained audit log with integrity check; administrators manage the platform but cannot see content,
- nightly backups with regular restore tests, and export via WebDAV, CalDAV and CardDAV,
- operation in Germany: office, video meetings and speech recognition run on nest54’s servers; for core operations, the data centre is the only service provider,
- a data processing agreement that administrators conclude directly in the platform.
What nest54 cannot do: risk analysis, incident handling, reporting, training and management responsibility remain your company’s tasks. nest54 does not currently hold ISO 27001 or BSI C5 certification; these are planned as targets for the cloud service. Read more about security and data protection under Security.
Frequently asked questions
Since when have NIS2 obligations applied in Germany?
The German implementation act entered into force on 6 December 2025. According to the BSI, there is no general transition period. Covered entities must register no later than three months after they first fall within scope.
Which reporting deadlines apply to a security incident?
Under Section 32 BSIG: an early initial report no later than 24 hours after becoming aware of a significant incident, an incident report no later than 72 hours, and a final report no later than one month after the incident report. Interim reports are due at the BSI’s request.
Does NIS2 affect companies that are not covered themselves?
Indirectly, yes. Covered entities must address the security of their supply chain. The BSI points out that this can affect suppliers, for example through contractual requirements.
Does a particular collaboration tool make a company NIS2-compliant?
No. A tool can support technical measures such as multi-factor authentication, encryption or logging. Risk analysis, incident handling, reporting, training and management responsibility remain with the company.
Sources
- Cybersicherheitsrecht: NIS-2-Umsetzungsgesetz ab morgen in Kraft (press release, 5 December 2025, German) – Federal Office for Information Security (BSI)
- Fragen und Antworten zu NIS-2 (FAQ, German) – Federal Office for Information Security (BSI)
- NIS-2-Betroffenheitsprüfung (applicability check, German) – Federal Office for Information Security (BSI)
- BSI Act (BSIG), Sections 28, 30, 32, 33, 38, 65 and Annexes 1 and 2 (German) – Federal Ministry of Justice / gesetze-im-internet.de
- Directive (EU) 2022/2555 (NIS2 Directive), Articles 21, 41 – EUR-Lex